
Keep control of your encryption keys, in the UK, under UK jurisdiction.
UK-hosted Luna Cloud HSMs from Thales are now available,
meaning you can move sensitive workloads to the cloud without giving up sovereignty.
UK sovereignty is more than data residency
Many cloud providers can tell you where data is stored.
Few can prove who controls the cryptographic keys protecting it.
For regulated UK organisations, key control is often the difference between meeting sovereignty requirements and simply meeting residency requirements.
UK-hosted Luna Cloud HSMs ensure cryptographic keys are generated, stored, backed up, used, and destroyed entirely within the UK, providing a clear and defensible control boundary.
UK cloud control starts with the keys
A UK region tells you where the service runs. It does not always tell you who controls the trust boundary.
Which laws apply to the provider running the infrastructure?
Who on the provider side can access operational systems?
Where are keys generated, used, backed up and destroyed?
For regulated workloads, those details matter. With UK-hosted Luna Cloud HSMs on the Thales DPoD cloud marketplace, customer keys for the UK-based service are generated, used, backed up and destroyed in the UK in customer-controlled partitions. A cloud HSM control boundary you can point to.
Outcomes you can now deliver with UK-hosted Luna Cloud HSMs
Prove sovereignty, not just residency
Provide evidence to regulators, auditors and risk committees that the full key lifecycle sits under UK jurisdiction
Unblock stalled cloud programmes
Give security, risk and compliance teams a defensible answer to the "who controls the keys?" question
Migrate regulated workloads with confidence
Move sensitive services into cloud without redesigning your trust model
Reduce third-party and concentration risk
Separate cryptographic control from your cloud provider's control plane
Stay ready for what's next
Build a clear key-control model today that makes post-quantum migration significantly more manageable tomorrow
Consume security at cloud speed
No dedicated hardware to procure, deploy or operate for each new use case
Stay in control amid regulatory and geopolitical change
Sovereignty is now a boardroom issue, while cross-border data access laws, concentration risk and national resilience concerns mean UK organisations must evidence control over their keys, not just assert it.
UK-hosted Luna Cloud HSMs are built for this moment: proven technology, brought under UK sovereign control — and aligned with UK GDPR, NCSC Cloud Security Principles, TSA, FCA/PRA, DORA and NIS.
Sovereign key protection,
across your critical use cases
Protect applications and data
Application encryption, database key protection, sensitive data protection
Secure identities and access
PKI, certificate authorities, digital and device identities
Safeguard transactions and software integrity
Digital signing, code signing, software supply chain, high-value transactions
Enable confident cloud migration
Consistent key management across on-premises, cloud and SaaS
One Luna HSM trust model, multiple ways to deploy
On-Premises - Luna HSM
Maximum control. Your hardware, your data centre, your rules.
Cloud - UK-Hosted Luna Cloud HSM on DPoD
HSM-as-a-Service. Dedicated HSM resources with simplified operations and sovereign key lifecycle management in the UK.
Hybrid - Hybrid Luna HSM
Combine on-premises and cloud HSMs for greater flexibility, resilience, and sovereignty.
Choose the deployment model that fits your business, while maintaining consistent security and crypto agility across environments.
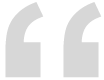
“Cloud adoption has moved beyond questions of where services are hosted. Organisations increasingly need to know who controls the cryptographic keys protecting their most valuable applications, identities and data,”
Paul Hampton
Data Protection Cloud Services Owner
Get in touch with an expert
Or start your free trial HERE
Discuss Your UK Sovereignty Strategy
Talk with a Thales expert about maintaining control of encryption keys, meeting regulatory requirements, and reducing sovereignty risk.
More resources for you

Solution Brief: UK-Hosted Luna Cloud HSM for Trusted Cloud Adoption

Blog: UK Cloud Control - Why Sovereignty Has to Move Beyond Data Location

White Paper: Navigating Digital Sovereignty in an Era of AI and Geopolitical Uncertainty

eBook: Achieve Digital Sovereignty with Thales
Blog: The Impact of AI on Digital Sovereignty


Copyright © 2026 Thales. All Rights Reserved